Skip to content

Agentic penetration testing

Agentic pentesting.Built to go deeper.

DeepScan agents pursue attack paths and validate exploitability. Your team sets the objectives, directs testing, and reviews the evidence.
  • Continuous testing
  • Production-safe
  • Proof of exploit
  • Attack chains
  • Fix retests
  • Web · API · Mobile
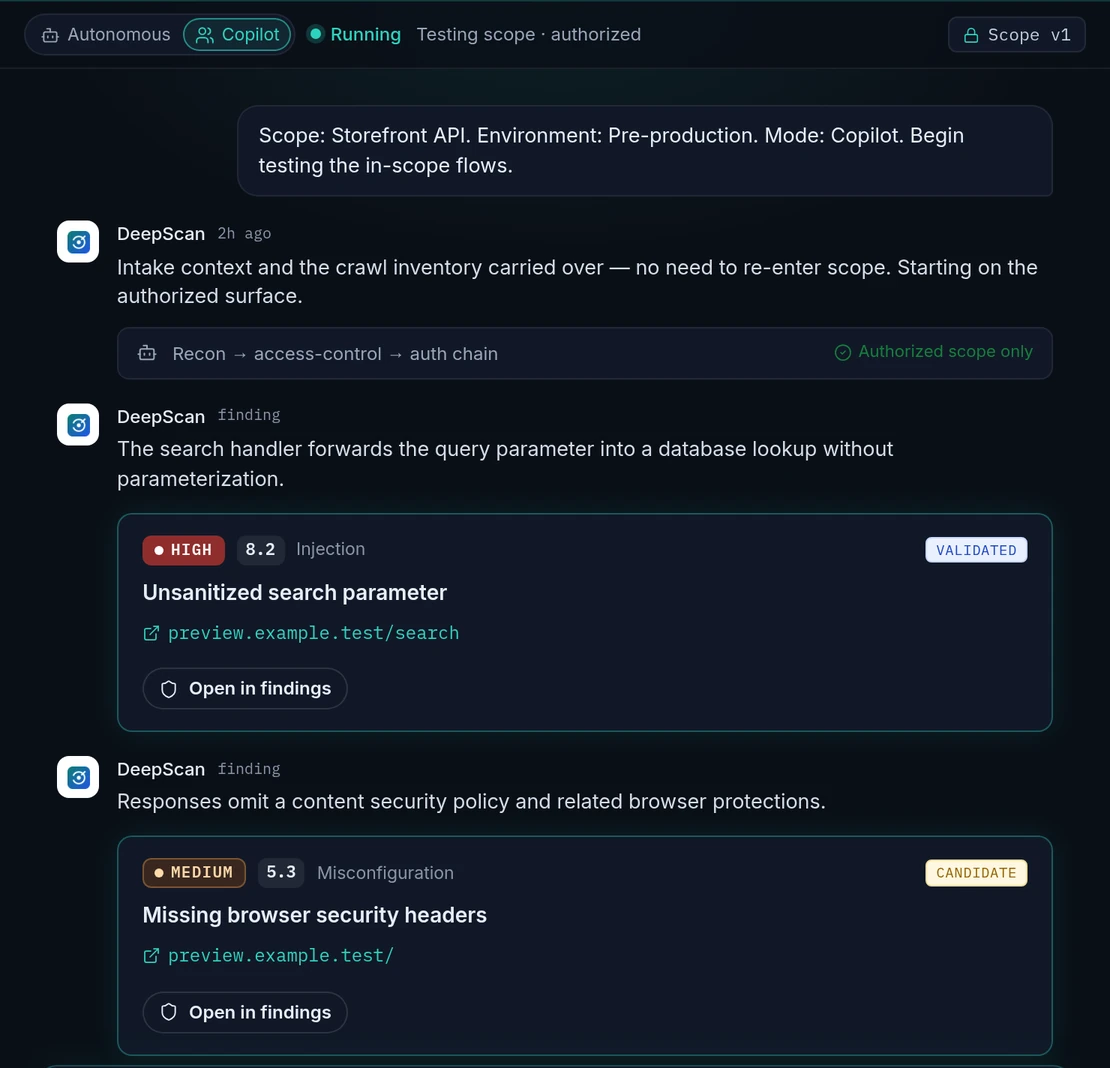
DeepScan testing chat in Copilot mode: agents follow the recon to access-control to auth chain and surface a validated high-severity finding with evidence.
Illustrative · sample data

How it works

Your team directs. Agents go deeper.

  1. 01

    Set objectives

    Your team sets the objectives and the approved scope for each test.

  2. 02

    Agents chase attack paths

    Specialized agents move from individual weaknesses to attack chains and validate exploitability.

  3. 03

    Review the evidence

    Your team steers the run and reviews the evidence behind each finding.

Attack chain · validated

  1. Low-privilege accountValidated
  2. Role escalationValidated
  3. Restricted recordsValidated
Outcome
  • Confirmed finding · Broken access control
  • Evidence attached
  • Fix ready

Built for production

Safe to run. Always on.

  • Continuous

    Test every release, not once a year.

  • Production-safe

    Rate limits, test windows, approved scope.

  • Proof of exploit

    Validated with evidence before release.

  • Fix verified

    Retest each finding from its original steps.

Live testing

Autonomous pentesting. Expert control.

Agents run the test. Your pentesters steer in Copilot and confirm every finding.
  • Autonomous
  • Copilot
  • High · Confirmed
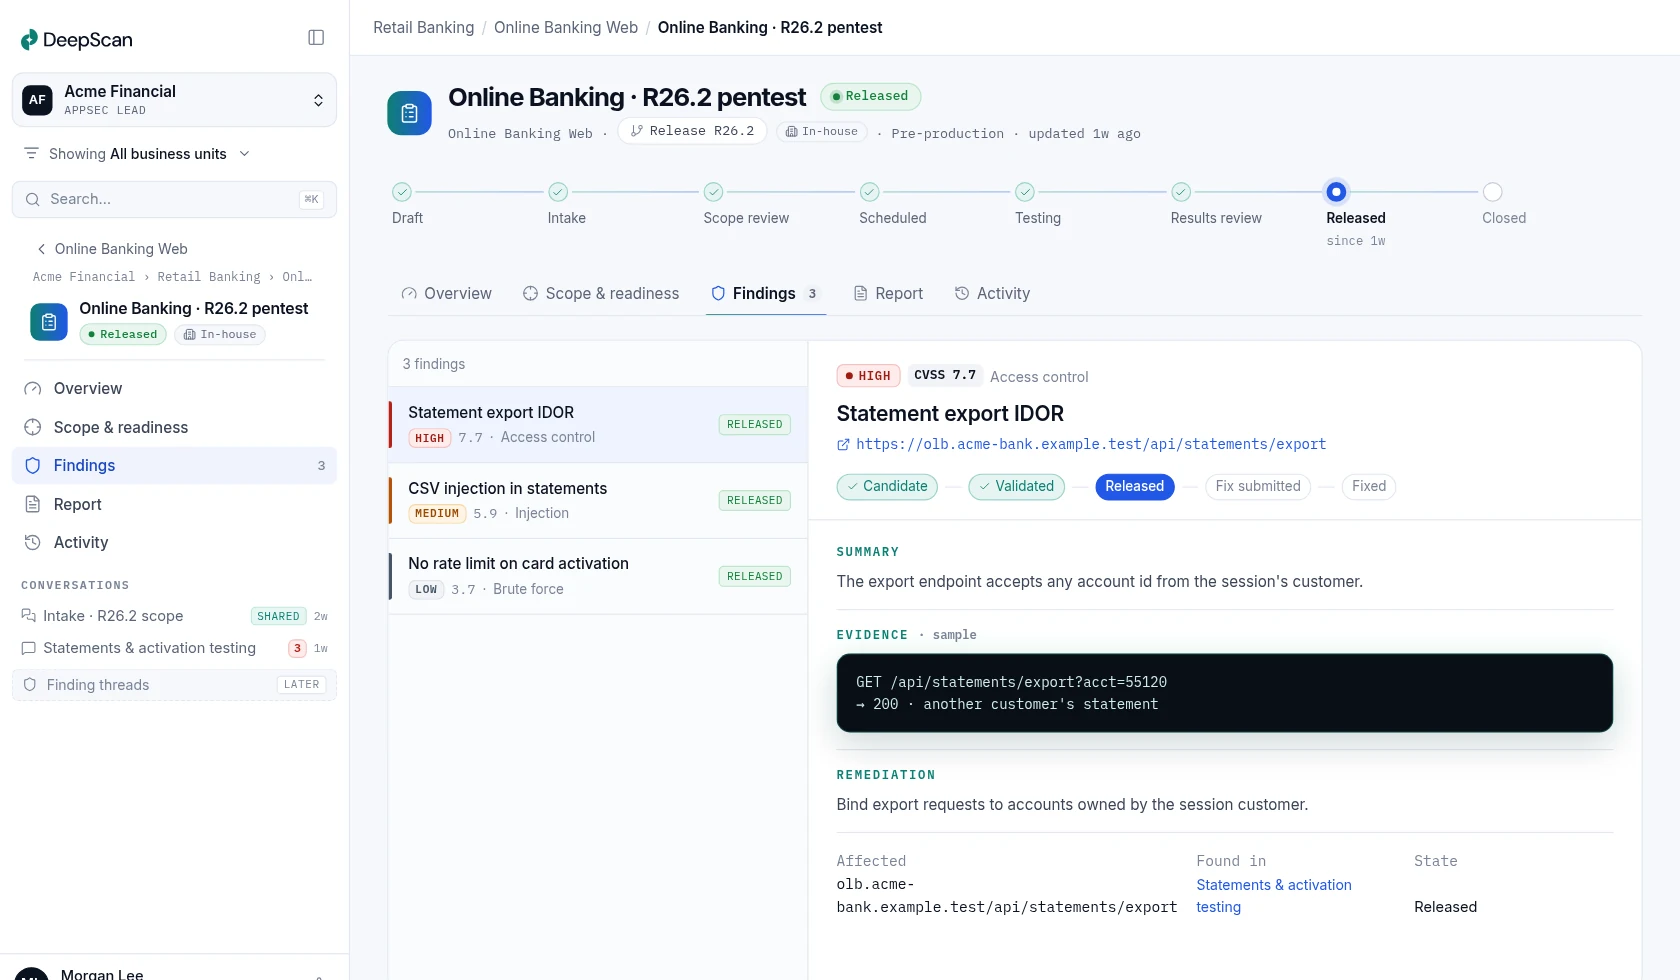
DeepScan findings review with evidence, remediation and retest state.
Illustrative · sample data

Built for

One platform. Every pentest program.

For AppSec teams

Clear the pentest queue.

Requests arrive scoped. Agents test. Your team releases the evidence.

  • Scoped requests
  • Validated findings
  • PTaaS subscription
Explore AppSec
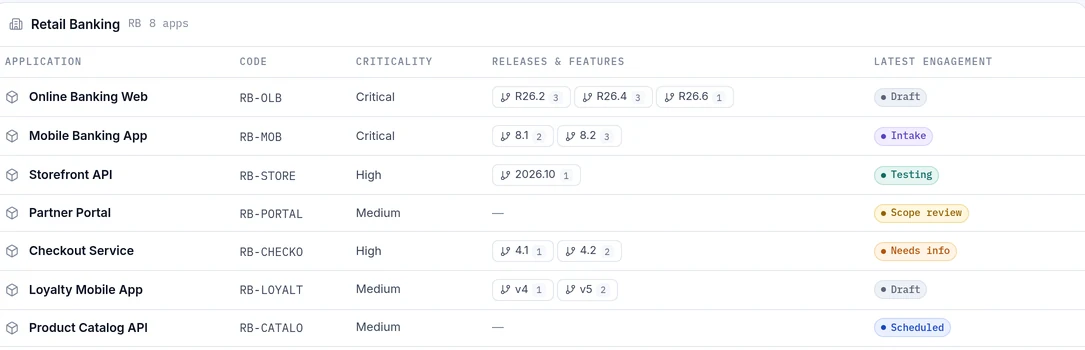
DeepScan applications catalog with the latest engagement state per app (sample data).

For Red Teams

Pursue the next attack path.

Steer agents from single weaknesses to attack chains.
  • Attack chains
  • Copilot steering
  • Evidence per path
Explore Red Teams
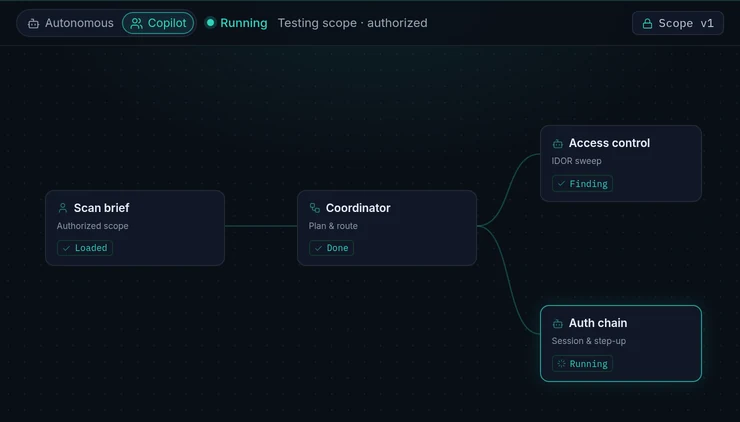
DeepScan attack-path graph during a Copilot run (sample data).

For MSSPs & pentest firms

Scale testing without scaling headcount.

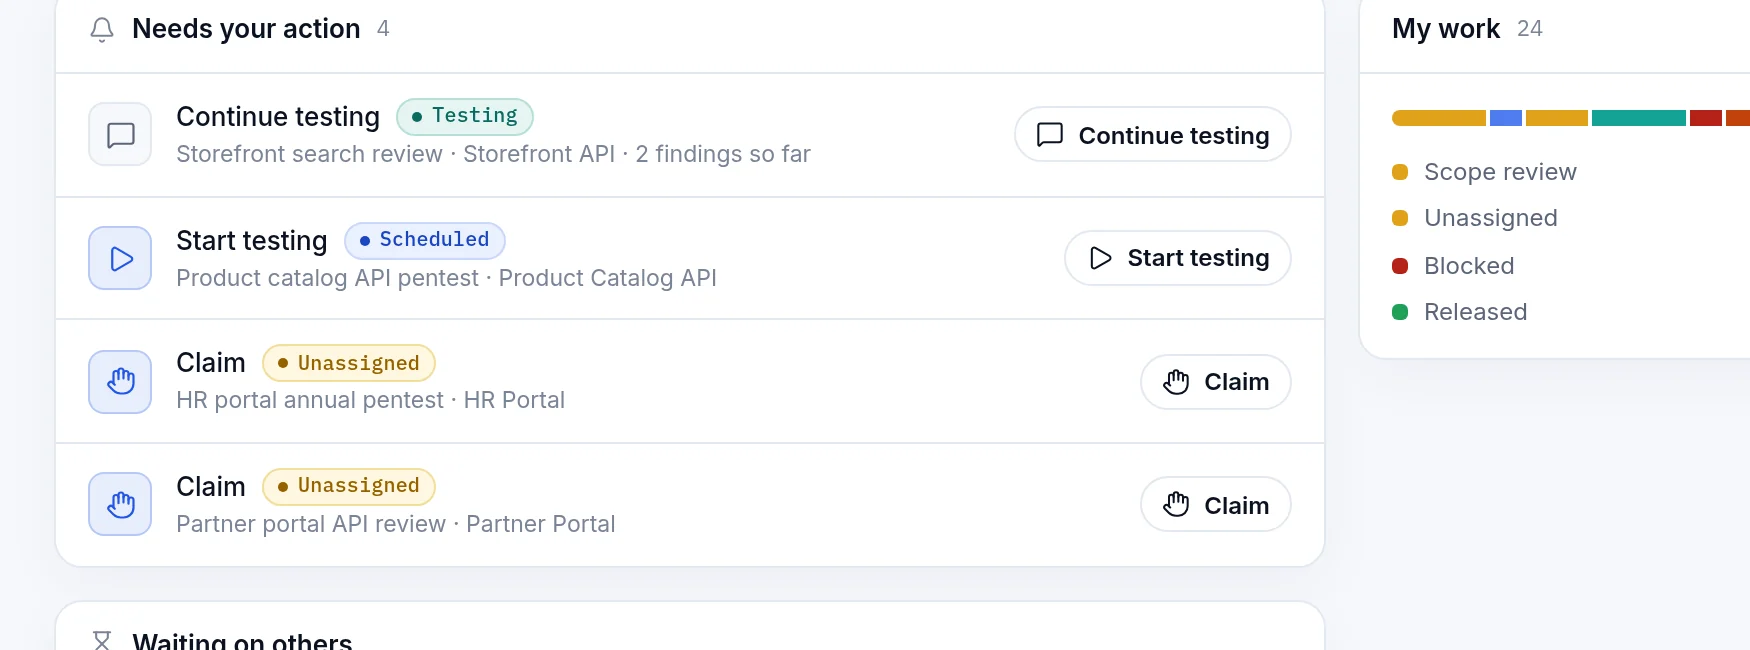
Agents handle recon, scanning and attack chains. Testers run more engagements in parallel.
  • Parallel tests
  • Tools ready
  • Production-safe
Explore MSSPs
DeepScan tester queue with several engagements to continue, start or claim (sample data).

For Compliance

Audit-ready pentests, on schedule.

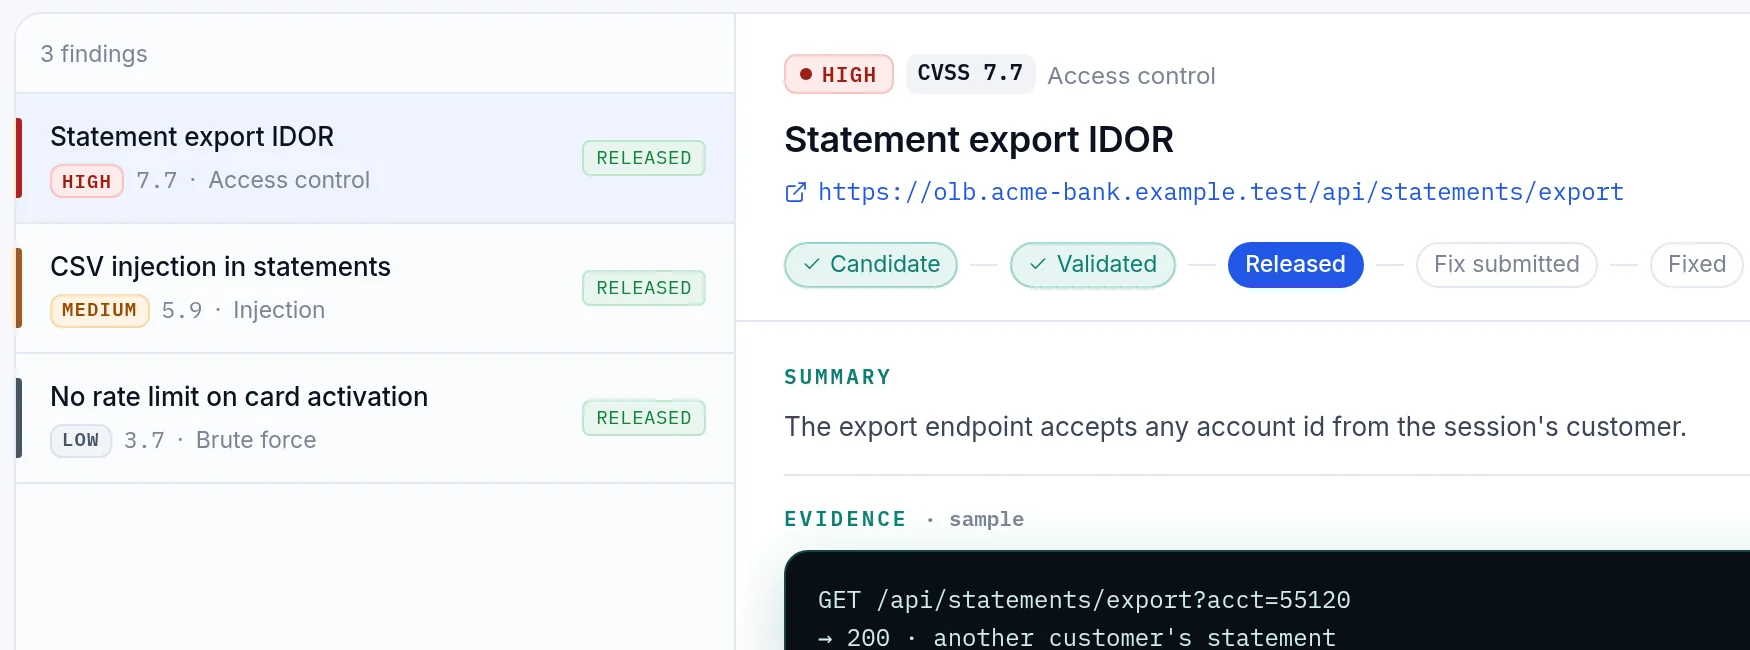
Scope for SOC 2 or ISO in minutes, test, retest and hand auditors the evidence.
  • SOC 2 / ISO scoping
  • Retests included
  • Evidence report
Explore Compliance
DeepScan findings review with severity, validation state and evidence (sample data).

Control & safety

Your objectives. Your boundaries.

01

Approved scope

Agents test only the scope your team approves.

Scope v2 · approved
02

Human control

Your team sets objectives, directs testing, and steers the run.

Copilot · pause · redirect
03

Traceable evidence

Every finding carries evidence your team can review.

High · validated · evidence

Expert-led services

Need a formal pentest? Add our experts.

CREST Pathway Company
  • Web
  • APIs
  • AI/LLM
  • Cloud
  • Mobile
Explore services →

Get started

Run the pentest in DeepScan.

Approved for frontier AI cyber programs

  • AnthropicCyber Verification ProgramApproved Apr 2026
  • OpenAITrusted Access for CyberApproved Aug 2026 · Daybreak Blue tier